macOS Screen Sharing Vulnerability CVE-2026-65400: Attackers Bypass Authentication to Compromise Macs
Cybersecurity, macOS Vulnerabilities, Remote Access Security
macOS Screen Sharing Vulnerability CVE-2026-65400: Attackers Bypass Authentication to Compromise Macs
A Mac Security Vulnerability Every Business Should Understand
Apple computers have earned a reputation for strong security. However, no operating system is immune to vulnerabilities, particularly when legitimate administrative features introduce remote access into the environment.
A recently disclosed vulnerability in Apple's macOS Screen Sharing feature demonstrates why organizations must evaluate remote access services as carefully as any other entry point into their networks.
The vulnerability, identified as CVE-2026-65400, allows a network-based attacker to potentially authenticate to macOS Screen Sharing without valid credentials.
Apple released security updates on August 6, 2026, to address the issue. Subsequent reporting in August documented active exploitation against internet-exposed Macs, including incidents involving unauthorized root access and cryptocurrency mining software.
For businesses using MacBooks, iMacs, Mac minis, or other Apple computers, the implications extend beyond a single vulnerable application.
An improperly secured remote access service can create an opportunity for attackers to compromise endpoints, interfere with operations, and potentially expose business information.
The lesson for business leaders is straightforward: a trusted operating system does not eliminate the need for continuous vulnerability management, access controls, and security oversight.
What Is CVE-2026-65400?
CVE-2026-65400 is an improper authentication vulnerability affecting the built-in Screen Sharing functionality in macOS.
Screen Sharing is a legitimate remote access capability that allows an authorized user to view and control another Mac across a network.
Organizations use this functionality for IT support, troubleshooting, remote administration, and accessing systems that operate without a dedicated monitor.
Under normal circumstances, access requires appropriate authentication.
CVE-2026-65400 undermines that security boundary.
According to the vulnerability disclosure, an attacker with network access to an affected Screen Sharing service may be able to authenticate without possessing valid credentials.
Apple addressed the issue through improvements to authentication state management, which is responsible for maintaining and validating the state of an authentication process.
Vulnerability overview
Security detail | Information |
|---|---|
CVE identifier | CVE-2026-65400 |
Affected component | macOS Screen Sharing |
Vulnerability type | Improper authentication |
Attack vector | Network |
Common service port | TCP 5900 |
Security consequence | Unauthorized remote access |
Initial patch release | August 6, 2026 |
Exploitation reported | August 2026 |
Importantly, this vulnerability does not mean every Mac is remotely accessible to an attacker.
The exposure depends on factors including the macOS version, whether Screen Sharing is enabled, and whether an attacker can reach the vulnerable service.
Nevertheless, systems with Screen Sharing exposed directly to the internet represent a particularly concerning configuration.
Attackers Have Already Exploited the Vulnerability
The risk associated with CVE-2026-65400 is not limited to a theoretical demonstration.
On August 14, 2026, BleepingComputer reported that the Netherlands' National Cyber Security Centre had identified active exploitation of the vulnerability.
The reported attacks targeted systems with Screen Sharing accessible from the internet through TCP port 5900.
In the incidents described by the Dutch authority, attackers obtained root access and installed Monero cryptocurrency mining software.
Root access represents the highest level of privilege on a Unix-based operating system such as macOS.
That makes the reported outcome particularly significant.
An attacker operating with elevated privileges may be capable of modifying system configurations, accessing sensitive resources, installing unauthorized software, or weakening security controls.
However, the publicly reported incidents should not be interpreted as proof that every exploitation attempt results in root access or that attackers have compromised every category of business data.
The confirmed reporting establishes a serious compromise scenario, not an unlimited set of observed outcomes.
Why cryptocurrency mining matters
Cryptocurrency mining may appear less threatening than ransomware or data theft, but unauthorized mining software is evidence that a system's integrity has been compromised.
It may also consume computing resources, degrade performance, and interfere with legitimate workloads.
For business leaders, the critical question is not simply whether the attacker installed a cryptocurrency miner.
It is whether the organization can determine how the attacker entered, what privileges were obtained, what else occurred, and whether the system can be trusted afterward.
Which macOS Versions Are Affected?
Apple released fixes for CVE-2026-65400 across three supported macOS product lines.
The following versions contain the initial security fix:
macOS release | Version containing fix |
|---|---|
macOS Tahoe | 26.6.1 |
macOS Sequoia | 15.7.9 |
macOS Sonoma | 14.8.9 |
These are the versions in which Apple addressed the vulnerability in August 2026. Organizations should install the latest applicable security updates available for their supported macOS release, rather than treating these historical patch levels as the final update target.
Businesses should also review older Mac devices and unsupported operating systems separately.
A device that cannot receive an applicable security update requires a documented risk decision, compensating controls, or replacement.
Why This Vulnerability Matters to Businesses
The business implications of CVE-2026-65400 extend beyond personal computer security.
Many organizations now operate mixed Windows, macOS, cloud, and mobile environments.
Mac computers frequently access the same sensitive business applications and information as Windows endpoints.
These resources may include financial records, customer information, legal documents, cloud applications, internal communication platforms, and administrative tools.
An attacker who compromises a Mac may gain opportunities to interact with resources available through that device, depending on the user's permissions and other security protections.
Three business risks deserve particular attention.
1. Unauthorized access to business systems
A compromised endpoint may expose information or applications accessible through an active user session.
For organizations handling confidential client information, the potential impact can include privacy, contractual, and regulatory concerns.
2. Elevated privileges and system integrity
The reported root-level compromises illustrate why authentication failures in remote access services deserve immediate attention.
A privileged compromise may allow an attacker to make changes that ordinary users cannot.
Organizations must therefore assess both unauthorized access and the integrity of the affected device.
3. Incomplete visibility into Mac security
Some businesses maintain mature Windows security programs but apply less consistent oversight to their Mac environments.
This can result in incomplete asset inventories, delayed patching, unnecessary remote services, and inconsistent endpoint monitoring.
Mac computers are business endpoints and should be governed by the same security standards as every other corporate device.
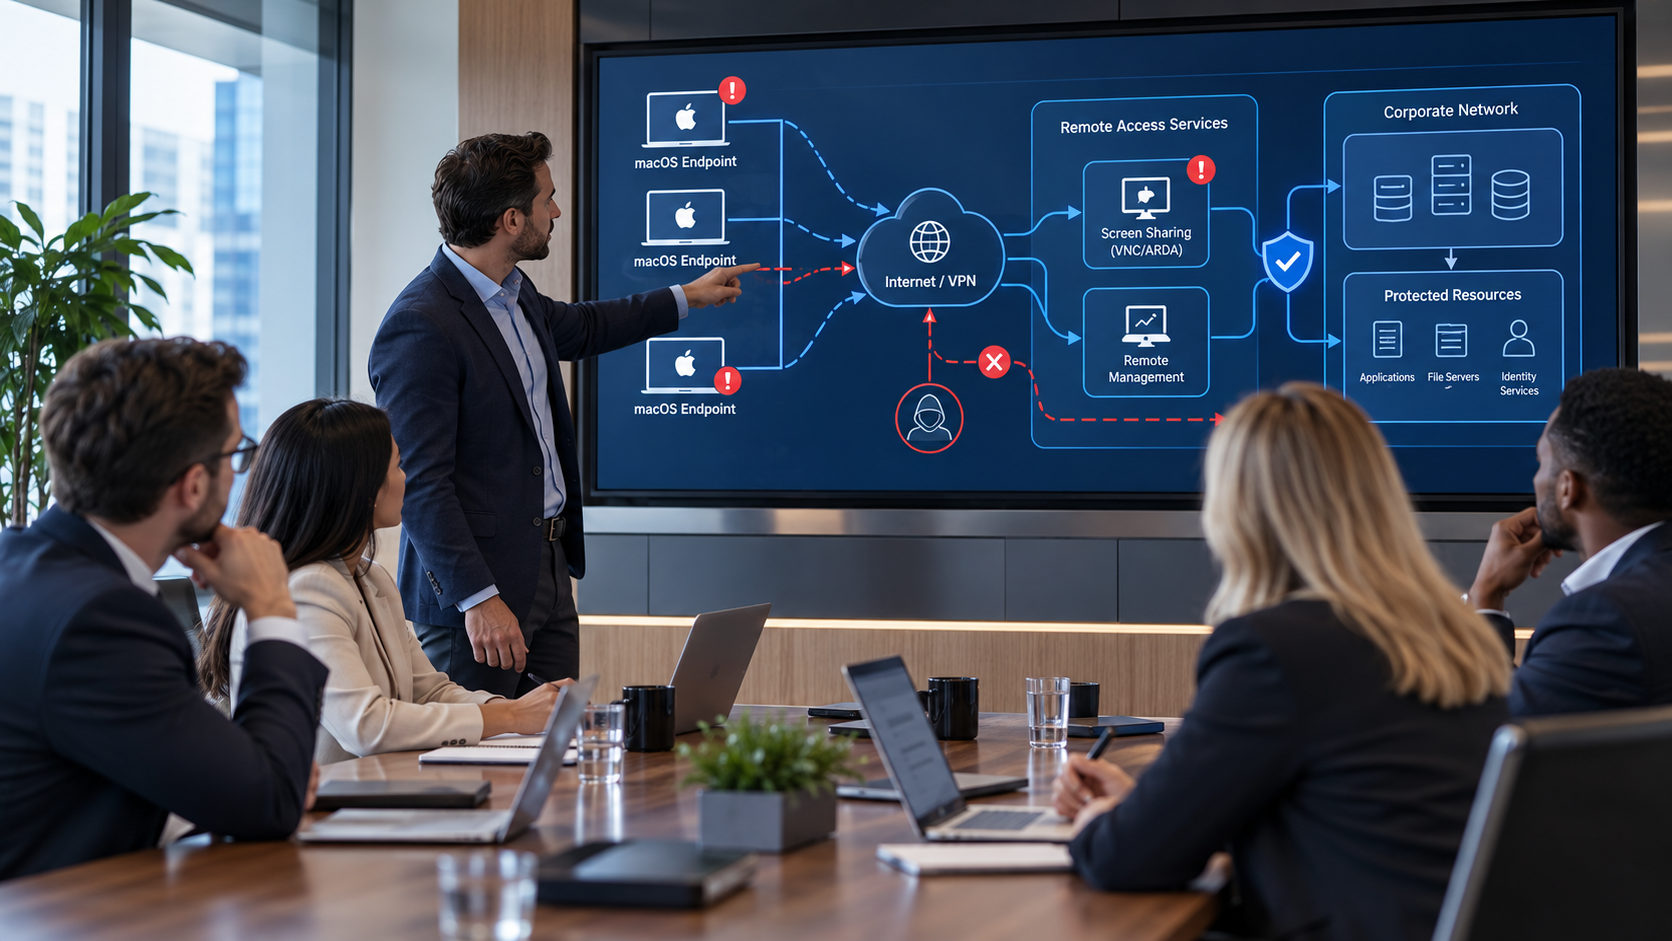
Network segmentation and restricted remote access minimize the blast radius of macOS vulnerabilities.
How Businesses Can Protect Their Mac Computers
The most effective response combines patch management, reduced network exposure, endpoint monitoring, and incident-response readiness.
1. Apply the appropriate macOS security updates
Start by identifying every Mac used for business operations.
Determine its operating system version and verify that the relevant security updates have been installed.
Users can generally check for available updates through:
System Settings → General → Software Update
For managed business environments, IT administrators should verify installation through their endpoint management or mobile device management platform.
Do not assume an update was successfully installed simply because it was assigned or made available.
2. Disable Screen Sharing when it is unnecessary
Remote access capabilities should not remain enabled by default without a documented business purpose.
On supported macOS versions, administrators can review Screen Sharing through:
System Settings → General → Sharing → Screen Sharing
If the feature is unnecessary, disable it.
If Screen Sharing is required, restrict access to approved administrators and appropriate management networks.
3. Restrict access to TCP port 5900
The reported exploitation activity involved internet-exposed Screen Sharing services.
Businesses should review firewalls, router configurations, VPN policies, and network access rules to identify unnecessary exposure.
TCP port 5900 should not be openly accessible from the internet merely for administrative convenience.
Restricting network access reduces exposure, but it does not replace the need to install the security update.
4. Monitor for unauthorized activity
Security teams should review available endpoint telemetry for suspicious activity, particularly on Macs that previously exposed Screen Sharing.
Relevant indicators may include unexpected remote access, unusual processes, unauthorized persistence mechanisms, abnormal CPU utilization, and unfamiliar software installations.
High CPU utilization alone does not establish that a cryptocurrency miner is present.
Organizations should investigate suspicious activity using endpoint detection tools, system logs, and established incident-response procedures.
5. Investigate suspected compromises before returning systems to service
If a Mac was running an affected version with an exposed Screen Sharing service, organizations should determine whether evidence of exploitation exists.
When compromise is suspected, preserve relevant evidence, isolate the device where appropriate, and conduct a structured investigation.
Simply installing the patch does not remove malware or reverse unauthorized changes that occurred before remediation.
What Business Leaders Should Ask Their IT Teams
CVE-2026-65400 presents an opportunity to evaluate whether existing security controls provide sufficient coverage for Apple devices.
Executives and business owners should be able to obtain clear answers to the following questions:
Do we have an accurate inventory of every business-owned and managed Mac?
Have the affected systems received the appropriate security updates?
Is Screen Sharing enabled on devices where it is not required?
Are any remote access services directly exposed to the internet?
Can our endpoint security tools detect suspicious activity on macOS?
Do we have a documented response procedure for compromised Mac computers?
Are Mac security controls included in our regular risk assessments?
These questions should be part of ongoing cybersecurity governance, not a one-time response to a vulnerability announcement.
The Bigger Cybersecurity Lesson: Remote Access Is a Security Boundary
CVE-2026-65400 reinforces an important principle of modern cybersecurity.
Remote access functionality is not inherently unsafe. In fact, it is essential to many business operations.
The risk emerges when remote services are exposed unnecessarily, authentication mechanisms fail, security updates are delayed, or organizations lack sufficient monitoring.
A defensible remote access strategy should include least-privilege access, network segmentation, timely patching, controlled administrative permissions, endpoint monitoring, and regular validation of security configurations.
These protections are particularly important for organizations operating hybrid workforces, distributed offices, and cloud-connected business environments.
Elliptic Systems' Perspective: Security Must Extend Across Every Endpoint
At Elliptic Systems, we emphasize a practical principle of cybersecurity risk management: organizations must understand what systems they operate, how those systems are accessed, and where security controls may fail.
The macOS Screen Sharing vulnerability illustrates why businesses should not rely exclusively on a platform's reputation for security.
Instead, organizations should maintain consistent cybersecurity oversight across Windows, macOS, mobile devices, cloud services, and remote access infrastructure.
Effective cybersecurity involves more than deploying software updates.
It requires visibility, governance, documented security standards, vulnerability management, and the ability to respond when protective controls fail.
For business leaders, CVE-2026-65400 is a reminder that cyber resilience depends on identifying and addressing security weaknesses before they become operational incidents.
If you would like to learn more about protecting your Mac computers and business environment against vulnerabilities such as CVE-2026-65400, schedule an appointment with Elliptic Systems here: https://ellipticsystems.com/discoverycall


